GDPR Compliance for WordPress Forms: A Practical Checklist
...
You just want a simple sign-up form with a name, an email, and maybe a phone number. So why does GDPR compliance in WordPress make it feel like you need a lawyer on speed dial? Consent checkboxes, privacy notices, retention periods, the “right to be forgotten”… where do you even start?
Most of what you’ll find online is a legal explainer written for companies with a compliance department, when all you want is a list of things to check on your form. You’re not even sure your little form counts. And in the back of your mind sits the email you’re dreading: “Please send me all the data you have on me, then delete it.”
Yes, it’s a lot. But the form part is a lot more manageable than it looks. Below is a plain-language GDPR checklist for your WordPress forms, and every item on it is a free setting you can switch on today.
What you’ll need
- Ninja Forms (free, and the only plugin this checklist uses)
Does GDPR apply to your WordPress form?
If your form asks for anything that identifies a person, like a name, an email address, a phone number, or a street address, and people in the European Union can fill it out, plan on GDPR applying to it. Where your site or your business is based doesn’t change that. An anonymous poll or quiz that collects nothing personal is a different story.
Donor forms, class registrations, volunteer sign-ups, and plain old contact forms all count. If a real person’s details come through it, it’s in scope. The European Commission’s data protection pages are the official place to read the rules themselves.
A quick word before we go further: we’re not lawyers, and this isn’t legal advice. Ninja Forms gives you the tools to handle the form side of your obligations, but no plugin can make a whole site GDPR compliant on its own. Your privacy policy and your cookie banner (a cookie consent plugin handles that part) matter too, and for a specific legal question, a lawyer is the right call.
Here’s what’s on the checklist. Skip on down to whichever one your form is missing.
- Tell people what you collect and why, right on the form.
- Ask for consent with a box they have to tick.
- Collect and store only what you’ll use.
- Stop keeping submissions forever.
- Be ready when someone asks for their data, or asks you to delete it.
Tell people what you’re collecting before they type a thing
GDPR expects you to tell people what you collect, why, and how long you keep it, in plain language, at the point where you collect it. The easy way is a short notice at the top of the form that links to your full privacy policy. An HTML field does the job in a couple of minutes.
No privacy policy yet? No worries. WordPress can create a starter privacy policy page for you to edit.
- Open your form, stay on the Form Fields tab, and click the blue (+) icon to open the Fields window.
- Add an HTML field from the Layout section and drag it to the top of your form.
- In the HTML field’s content box, write two or three sentences covering what you collect, why, how long you keep it, and that people can ask for a copy or deletion.
- End the notice with a link to your privacy policy.
Keep it short enough that people will read it. Here’s the notice on our demo form, a volunteer sign-up for a binturong rescue:
How we use your details: we use the information on this form only to schedule volunteer shifts at the rescue. We keep sign-ups for one year, then delete them. You can ask us for a copy of your data, or ask us to delete it, at any time.
Three sentences and a link. That’s all there is to it.
Ask for consent with a box they have to tick
Consent under GDPR has to be a clear, active yes. A Single Checkbox field that’s required and unticked by default gives you that, because the form won’t submit until the person ticks it. There’s no special “GDPR field” in Ninja Forms, and you don’t need one.
- Back in the Fields window, add a Single Checkbox field and drag it just above your Submit button.
- Give it a label that names the purpose, like “I agree to the Binturong Rescue storing my details to coordinate volunteer shifts.”
- In the field settings window, switch on Required Field.
- Leave the checkbox’s default as unchecked.
- Click Publish.
Resist the urge to tick the box for them. A pre-ticked box doesn’t count as consent under GDPR. Now when someone tries to submit without ticking it, the form stops them with “This is a required field.”
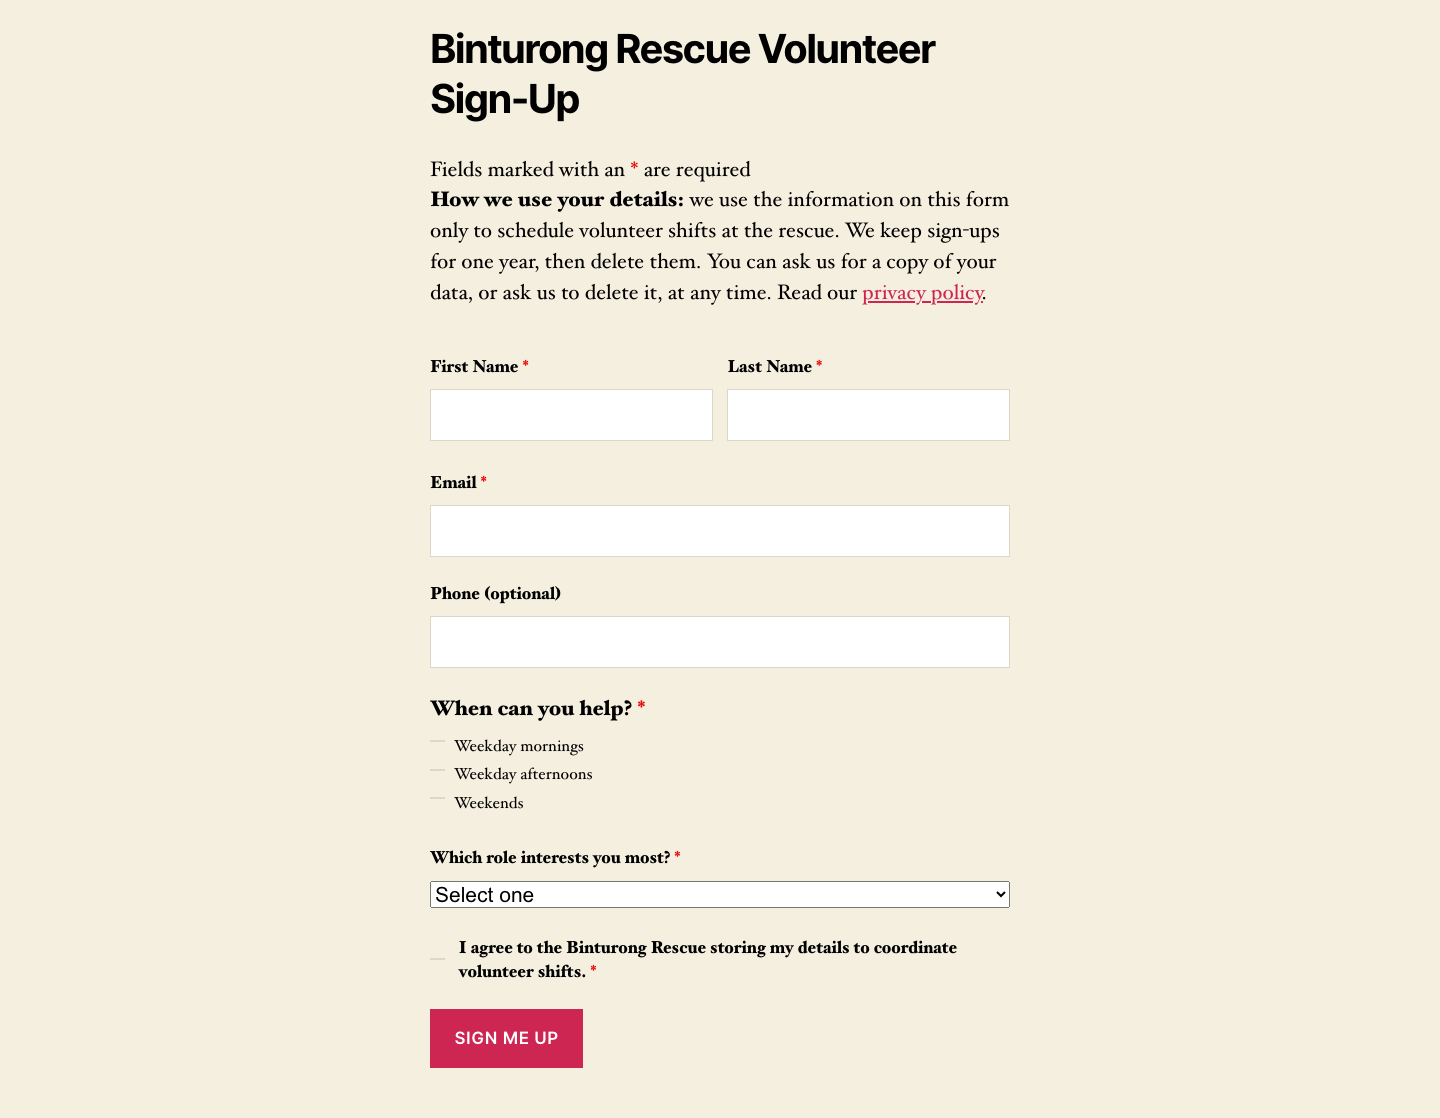
Our take? Put this checkbox on every form that collects personal details. It costs you one field, and it leaves no doubt about what someone agreed to.
Collect only what you’ll use
GDPR calls this data minimization, and it boils down to “if you don’t need it, don’t ask for it.” Take one pass through your form and delete any field you never look at. Make the nice-to-haves optional, the way the rescue labels its Phone (optional) field.
Sometimes you need a field for the notification email, but you don’t want it sitting in your database. The Record Submission action can leave that field out of what it saves.
- Click the Emails & Actions tab.
- Click the Record Submission action. On some older forms it’s called Store Submission.
- Expand the action’s Advanced accordion.
- Under Fields, leave Save All selected, then under Except, click Add New and pick the field to leave out.
- Click Publish.
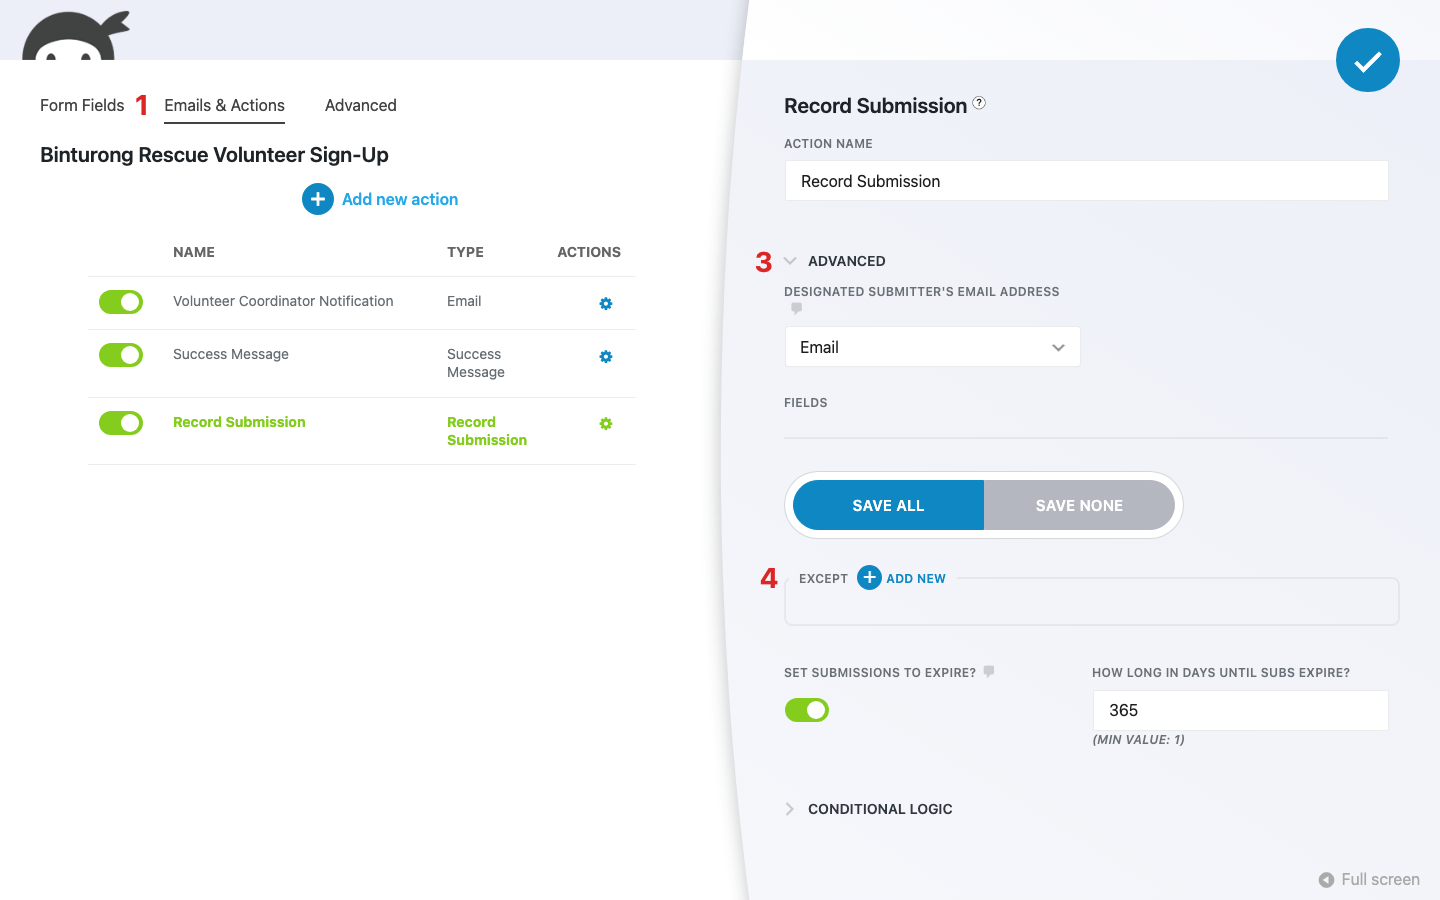
The submission still gets saved, with that field stored as “(redacted)”. Keep in mind that this setting only controls what goes into your database. The value can still go out in your notification emails, so remove the field from the email’s message as well if you want it gone everywhere.
You could also switch Record Submission off entirely on a form that only exists to send an email. We don’t recommend it for most forms. The data doesn’t disappear, it moves into inboxes, where it’s much harder to find, export, or delete when someone asks.
Stop keeping submissions forever
GDPR says you shouldn’t keep personal data longer than you need it. Ninja Forms can clear out old submissions for you on a schedule, form by form. Turn on Set Submissions to expire and choose how many days to keep them.
Think of it like shredding old paperwork on a schedule instead of letting the filing cabinet fill up. Match the number to whatever your privacy notice promises. The default is 90 days, and the rescue uses 365 to line up with the “one year” in its notice.
- Back in the Record Submission action’s Advanced accordion (pictured above), switch on Set Submissions to expire?
- In How long in days until subs expire?, enter the number of days to keep submissions.
- Click Publish.
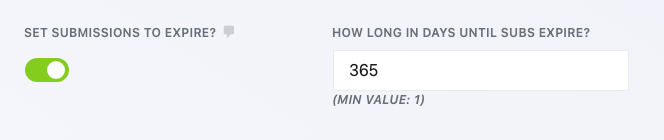
Once a day, Ninja Forms moves submissions older than your limit into the trash under Ninja Forms > Submissions. They aren’t permanently gone at that point. WordPress normally empties the trash after 30 days, and you can take it out sooner yourself whenever you like.
Give Ninja Forms a try today!
Ninja Forms is free! Optional premium features available with any membership.
Someone asked for their data. Now what?
WordPress has built-in privacy tools for this, and Ninja Forms plugs straight into both of them. Enter the person’s email address, and WordPress pulls in every Ninja Forms submission containing that address along with the rest of their data. You don’t have to set anything up first.
- In your WordPress admin, go to Tools > Export Personal Data for a copy, or Tools > Erase Personal Data for a deletion.
- Enter the person’s email address, choose whether to send them a confirmation email, and click Send Request.
- Once the request is confirmed, hover over it in the list and click Download personal data or Force erase personal data.
The export includes a Ninja Forms Submission Data section listing every field from each of their submissions, labeled by form. Erasing deletes those submissions permanently, with no stop in the trash along the way.
One thing to watch: both tools match the email address anywhere in a submission. If a form has a “refer a friend” field, a friend’s erase request removes the whole submission that mentions them. Run an export first and you’ll see which submissions will go before you click anything permanent.
Let people send requests from a form
If requests come in often, Ninja Forms includes Export Data Request and Delete Data Request forms that file the request in Tools for you and email the confirmation link. The delete version can also anonymize a submission instead of deleting it. Personal fields get overwritten with “(redacted)” and everything else stays, so the rescue would still know how many people signed up for weekend shifts.
Anonymizing relies on two settings on your everyday forms. Each personal field needs This Field Is Personally Identifiable Data switched on in its Advanced settings, and the Record Submission action’s Designated Submitter’s Email Address needs to point at your Email field. The Ninja Forms GDPR documentation lists which field types carry that first setting.
When you’re ready, you can set up self-service export and delete requests in a few minutes, anonymize option included.
Give your WordPress form a GDPR compliance checkup today
Like we said at the top, GDPR compliance in WordPress can feel like a job for a legal team. The form part isn’t. A notice, a checkbox, a trimmed field list, an expiry date, and a plan for requests, and your form is holding up its end.
You don’t need a compliance department or a paid add-on to do right by the people who fill out your forms. Open the form that collects the most personal details and start with the consent checkbox. You can do it.
Try Ninja Forms Today
Always free, with premium features available through our memberships.
Typical EU regulation stuff. Are you required to collect the same consent though when the users send you an e-mail themselves? I mean, when you display your e-mail address on your contact page?
Norbert,
I can’t imagine the GDPR would apply to routine email exchanges/conversations. Technically their email address would be stored by the email client you’re using, but that would seem a stretch to call data collection on your part.
Cheers,
Quay
That sounds relieving for some of us. Thanks for being so proactive!
If you, as a business, organisation, charity etc, provide a means of communication which may mean the ‘processing’ of personal data, then the GDPR will apply. The email client in this regard would have to be compliant. Ensure that you evalutate your organisations collection of personal data and craft your unique privacy policy (‘Fair Processsing Notice’), to allow visitors to your site the choice. Processing of personal data under the GDPR has to be fair, lawful and transparent.
In particular relation to forms, even with the ‘do not store’ option, you have to be able to demonstrate that the receiving system/organisation is compliant with the GDPR. So additionally check the hosting provider and how they are preparing for the GDPR as they will be data processors (by hosting your site), and you will no doubt be classified as the data controller. Remember under the GDPR if there any data breaches, both parties could be liable.
Excellent article, really clarifies it all thanks. Cant seem to find any practical tips for web developers out there to comply, about what we actually need to physically do! It seems quite simple really now, despite all the scaremongering out there!
Just wondering would the same methods above suffice for ecommerce sites storing order & customer data (using WooCommerce + Ninja Forms addon for example ) by simply adding an extra checkout filed with description & checkbox?
Thanks again!
John
John,
Hey! I don’t think you’d even need to add an extra checkout. As long as you meet the criteria laid out in the article somewhere in your normal checkout process, you should be good.
– state that you’re collecting data, let them know what data, and request consent in an obvious, explicit, and plainly spoken fashion
– make certain you’re storing that data in such a way as that it can be linked back to that user for future deletion on their request
– provide an easy way for them to request that you no longer collect data on them, delete collected data, or provide a copy of collected
data
Cheers,
Quay
Great article!
Something I’m still not 100% clear on.
If someone uses your website form to contact you to get a quote/ find out more about your services, are you able to call/email them back without infringement? Does the fact that they filled out the form imply consent?
Shea,
Thanks! It’s my understanding that you must explicitly request and acquire consent no matter the intended purpose of the form. If personal data of any sort is being collected, implied consent is not enough to satisfy the requirement.
Cheers,
Quay
If the form is a contact form for potential customers inquiring about a product, and they get sent a copy of what they submitted at the time they submit (along with consenting for their data to be stored for response and newsletter purposes) does this satisfy the access to data requirements, for that piece of data at least?
Sophia,
To the best of my knowledge, no. You need to be able to comply with any future request by that user to provide them with all personal data you have stored on them.
Cheers,
Quay
What about if you name an individual on your website in a testimonial?
Does this constitute the collection of personal data?
Do I need their explicit consent?
David,
Hey! If you’re using a quote from someone as a testimonial on your site I would definitely get their consent to do so first, but I would not think that would constitute personal data collection under the GDPR… however, that’s a better question for a legal professional than myself, unfortunately.
Cheers,
Quay
Yes you do. ANY information that can be directly related to a person must comply with GDPR (picture, ip address, name, phone number, email address,…)
Not just consented, but stored safely, available for them to read, and in simple way to view, download and request deletion.
If forms are hosted in the US but are embedded in your website hosted in the UK. If a user uses the form and submits the data, does that count as you sending their data out of the EEA? Or, because the user did it themselves does it count as them sending their own data out of the EEA and then the form platform sends it back into the EEA when you collect it? If I just had a statement under the form on the website that said “by clicking submit and ticking this box you consent to sending your data to a third party located outside of the EEA.”, would that cover us?
Any organization offering services to EU citizens MUST comply with GDPR. It’s not about where you come from, it’s about who you offer to.
Thanks for the article! As I understand it, consent is NOT always required. There are 6 legal bases for processing data, one of which is consent. Another is ‘Contract’, which would be appropriate if someone has requested a quote through your website – in this instance, a consent checkbox is NOT required.
Quoting from the ICO website:
“The GDPR sets a high standard for consent. But you often won’t need consent. If consent is difficult, look for a different lawful basis.”
“Avoid making consent to processing a precondition of a service.”
ICO website: https://ico.org.uk/for-organisations/guide-to-the-general-data-protection-regulation-gdpr/lawful-basis-for-processing/
Article I wrote on GDPR for WordPress websites (NB I’m not a lawyer!): https://hexagonwebworks.com/gdpr-wordpress-websites/
Thanks Sarah! That’s a really helpful addition to the conversation! 🙂
Cheers,
Quay
Your article is super helpful for formulating a plan of attack, Sarah – thank you!
Hello,
With regards to GDPR and things like anonymization or pseudonymization, how does that impact reporting/dashboard views? i.e. if a WordPress user has access to a view that list submissions they will be able to see PII.
Assuming that the user is “authorised” to view does this means that kind of data needs to anonymized in anyway?
Does data need to be stored encrypted etc in order to meet any technical requirements?
Thanks,
Andrew
Andrew,
Only individuals with Administrator level permissions can view Ninja Forms submissions.
To the best of my understanding after reading the text of the GDPR, data encryption is recommended as a best practise but not mandated for compliance.
Cheers,
Quay
Can you force the user to check the box to agree to marketing before the form submits?
You could hide the Submit button via Conditional Logic pending the box being checked, yes.
https://ninjaforms.com/extensions/conditional-logic/
Cheers,
Quay
Maybe a silly question here . . .
How does a web form logically validate an “EU Citizen” segment vs anyone else on the planet? Or should the form simply treat all users with the same opt-in dialog and backend processing?
There’s entire federal agencies that struggle to determine citizenship or residency.
Not silly at all!
There hypothetically are ways to validate where a user is located when form loads, for example with User Analytics by capturing IP. That would almost never be foolproof however. A visitor using a VPN for instance may not have their true IP captured by any tool you might employ.
The most direct route would be blanket application of the new guidelines, rather than trying to only focus on EU citizens. That’s a more effective approach that takes less work on your end, and you might just earn the appreciation of your non-EU users, too. Knowing that your website/organization/etc respects user privacy and personal data certainly won’t be taken as a negative by much of anyone 🙂
Cheers,
Quay
You can’t and that’s tricky part. Indirectly they made us all comply to “respect someone’s privacy” regulation.
Thanks for a helpful article!
I thought I read somewhere that it is important that the data stored is encrypted and even ‘separated’ eg. name is encrypted and stored separately from email address, date of birth or other sensitive data?
Also, I notice this comment form does not have a checkbox asking for our consent to store data. I guess you’re not feeling the need to comply just yet, or do you feel that this isn’t needed here?
Thanks again.
Glad you found it helpful!
– I’ve not read about the encryption/separation point. I do not believe that’s an aspect of the GDPR, but I am not legal counsel 🙂
– We’re still hammering out the finer points of implementing GDPR compliance ourselves! WordPress stores your name and email each time you comment, and that will definitely fall under the realm of the GDPR. Something along the lines of a consent request checkbox will probably be implemented in the future, and WordPress allows you to search and delete comments to comply with a user’s request to delete that data. That’s just thought spaghetti at this stage; as I said we’re still working through the details of everything we need to do before May as well!
Cheers,
Quay
Great article. We’ve been working hard on building a All in one GDPR plugin for WordPress to help website owners become compliant. Our plugin has an integration with Ninja Forms, to make this process even easier.
Check out the plugin here: https://gdprplug.in/
This article is misleading and wrong.
GDPR is not about websites it’s about user privacy. Follow me through:
I’m writing this text here and I am going to send it so you can all read it. I need to enter my name & email but there is no consent of mine that:
– states for which purpose I am giving my data (so “I consent to having ACME Inc collect my name and email” just wouldn’t be enough)
– there is no way for me to see my data, download and/or request deletion (to comply with the regulation those functions need to be made in SIMPLE way – not writing to NinjaForms an email, so they can copy-paste in their reply when they feel they have time – eg: there should be a place where I can enter my email and they should send me a link where I can see my data, download them and request deletion).
Next we have offline businesses; If you are not storing your submission forms online you are still using personal data from your forms to deliver goods or services to your customers – that storing and processing still counts. and needs to be recorded, consent, available to download and to request deletion.
Ranko,
I’m sorry you feel that way about the article, but I’d respectfully say that you’re misinterpreting our position here. I agree with you 100% that the GDPR is more about respecting user privacy that a technical manifesto. In fact, I’ve written an article that addresses exactly that point which we’ll be publishing soon.
The GDPR is a call for businesses around the world to step up and show a greater respect for the people they serve every day. We’re behind that completely, and are in the process of assessing and modifying so that our site meets those standards more thoroughly ourselves. I encourage you to check back with us soon to read more on our position.
Cheers,
Quay
I might also point out that this article is an overview of the GDPR. As a WordPress form builder product we are not trying to explain compliance in every area that the GDPR touches. We are trying to explain how you can be GDPR compliant with your use of Ninja Forms. As a product company, this is our chief concern for our users.
Thanks very much Quay.
Thank you so much Quay! We use WordPress for our blog and this definitely does help. I’ve been researching on the regulations for a while now and most guidelines are quite vague, at least to me. This does help a lot.
Glad to hear it!
The main issue with GDPR is the same issues we faced with the Cookie law a few years ago. In short, the people enforcing the law are unable to put into very plain language what is required. First I think the article is a good start, but there are some additional things to think about. So the first is that your compliance is as weak as your worse behaving Plugin or Theme. In other words what personal data (including ip) is being stored as a whole in the WordPress database. And more important than the consent aspects you need to access the risk in the case of a breach. Simply getting people to agree to store their data is not good enough. And the final part is anytime any part of WordPress, Plugins or Themes are updated, you have to go through the process all over again. The safest route is to take the attitude of only using the Plugins you absolutely need to. Also avoid any Plugins which are not absolutely transparent with how they work.
Thanks for your thoughts, Mark!
“The safest route is to take the attitude of only using the Plugins you absolutely need to.” stands out as very solid advice, particularly. Not just for the sake of the GDPR, but for a variety of reasons. General security not the least amoung them 🙂
Cheers,
Quay
Does Ninja Forms have an option to automatically delete captured data from the submission database after a set period of time?
As per the ICO’s Principle 5, which states: retain personal data no longer than is necessary.
This suggests that if a general inquiry has been dealt with it would be good policy to delete the data, this could be done via the deletion of the email but Ninja Forms also stores the data – can this be set to delete permanently after a set date?
We don’t, but after reading your comment and looking into the ICO a bit, I’ve submitted a formal feature request for this to our development team to consider. Thanks for your feedback!
Hi! How about if you don’t use a plugin for your enquiry forms and you simply receive an email with the inputted information? Do you need to change the way that works or does that fall under legitimate interest? Thanks!
Hello. Thanks for the article. I have a not unique use case in that we collect, store and pass our information via webhooks to a lead distribution platform that then sells leads to partners.
I am yet to find a truly useful article that clarifies how and if I am liable for how the information is used after it has left me (considering I was the original data holder).
Also, I use ‘Salient Theme’ and have major issues with the compatibility of the single checkbox field. It is either totally hidden (with one function of the theme selected) or such a small circle that its hardly seen and certainly not clickable.
Is there any support I could get for this to make sure I can continue using NFs.
Thanks
What happens to attachments? Are the encrypted on the server?
All data in your WordPress database is saved as plain text by default. That’s a WordPress-wide default. Database encryption is something you’ll need to implement if it’s needed/desired.
Thank you. Is there a plug-in or tool specific to NINJAForms available that encrypts the attachments that are uploaded by users of the specific forms?
Unfortunately, no. File Uploads stores uploaded files in your database unless you have it set up to save to an external source (and then it just ‘passes through’ the db en route to that source). Any database encryption should cover any of these files as well, but encrypting the WordPress database is a larger task than what fits within the scope of a forms plugin 🙂 … I wish I had some tools to recommend you. Something worth looking into in the future!
Hi,
I believe submissions received before the 25th May will also need to be re-consented if explicit consent was not given originally.
Is there an easy way of doing this with Ninja Forms?. Unfortunately I have already turned off store submissions and deleted submissions as mentioned in this article.
However, although the submissions are no longer stored in the WordPress database, the emails generated/sent from those submissions are likely still available in my Gmail. So is Gmail still considered ‘storing’ PII data and therefore I still need to add a opt-in checkbox for this even though I have ‘store submissions’ turned off?.
Andy,
Hey! I’m honestly not sure about ‘re-consenting’ previously collected data, but I’d think not. For sure though you’d still need a way to provide/delete previously collected submission data on request.
For email, with the caveat that I’m not legal counsel, to the best of my understanding email addresses in an inbox are not considered stored data on your part. Having a form that sends an email to a provided address but with storage disabled would qualify you as a processor under the GDPR since you re handling the data, but not a controller since you aren’t storing it (again, to the best of my knowledge).
Cheers,
Quay
In order to comply with the “right to know” and “forget me”.
Are you considering attaching to each field two bits of information .
1) this is a personal data field, 2) this is an email address field
Then it would be possible for you to implement the WordPress core filters that report and delete GDPR data.
Two obvious solutions to acquire the two bits of information
1) An admin page that lists all existing fields with two checkboxes
2) Add the check boxes to the Administration section for each field where you get the “field_key”
We’ve actually just released an update that leverages the WordPress Export/Erase features. The article’s now updated to reflect this. Thanks for your thoughts!
Cheers,
Quay
So, just so I know I’ve got this right…
1. If the user submitting the Delete Data Request form is a “registered” user (meaning they have an account/login for that specific WordPress install) then all one needs to do is head to the Erase Personal Data page in WordPress and click the “Delete” button.
2. If the user submitting the Delete Data Request form is NOT registered (meaning they do not have an account/login on that specific WordPress install) then that submission will just remain in the typical Ninja Forms Submissions location, and we’ll need to see it there, search for that email address in ALL of our Ninja Forms submissions lists and delete every instance manually?
Also, is there any sort of record of these deletions that Ninja Forms is producing? I guess I could just try all this out myself on my dummy sites, but figured its worth asking…
(Gosh all this GDPR stuff is a headache… lol)
Dustin,
Hey! That’s correct. The WordPress Export/Delete feature will identify all data associated with the verified email that’s handled by WordPress core- user meta, comments, etc. Plugins still need to hook into that feature to have it also handle data collected by the plugin. Right now we do in the case of registered users, so submissions data for those users will also be scooped up by the WordPress feature when using one of these forms or actions.
Ninja Forms will do this for non-registered users very soon as well. We’re actively working on that now, but it wasn’t shippable in time for this update. We didn’t want to hold up the rest for that one item, but it should be ready very soon and the registered/non-registered status won’t make a difference. We’re also working on a global submissions search feature to complement that. Afaik there’s no internal record being produced, but I’ll ask our dev team and update if I’m incorrect there 🙂
Cheers,
Quay
You say that simply not storing the data is the easiest way to comply, but if the content of the contact form gets sent to the company inbox, doesn’t that mean you’re storing the information there? The info I found online is a bit vague about this. Can I assume that a contact form that only sends info to an inbox doesn’t require GDPR consent?
Fred,
To the best of my understanding with the scenario you describe, the company is a processor of the data but the email existing in an inbox is not qualified as storage on your part. I’d like to be very careful to point out here that I’m not qualified legal counsel, but it appears to be a fair assessment that you’re acting as a processor rather than a controller in this regard.
The benefit to not storing the data is that you won’t have to worry about collecting it for export or deletion requests.
Cheers,
Quay
Is Ninja Forms content such as user name and email, accessible to google analytics? Can they “see” this information when the form is being submitted?
Lauren,
Not to be cheeky, but I would assume Google “sees” everything haha- regardless though, anything Google Analytics might pick up should not count as stored data on your part. That is of course to the best of my understanding as a non-attorney 🙂
Cheers,
Quay
Is there anything planned about retention/automated deletion? We reuse many of our forms on an annual basis or throughout the year and it would be useful if we could have a function to remove data after a certain period has elapsed, allowing us to comply with the retention periods we advertise on the site instead of doing it manually.
Yes! I actually just updated the article to reflect this. Look for it to be a standard feature very soon.
Cheers,
Quay
This is awesome. I can’t for the life of me figure why the WP core team left out a frontend form in the GDPR release.
Thanks NF Team for filling the gap with this.
Help! I added these new fields to be able to have my readers submit to remove their info. Which is great by the way. I got a submission today for a “delete data request” and was sent an email alert. I opened the submissions page and now I am unsure of what to do. I hit the delete info button next to the email. Does it send them a message that their info was deleted? Do I need to send them an email that I deleted their info? Do I save the email in the submissions area for proof? I am confused and I guess I need more instruction on what to do once we have a request and if we delete it how do we prove it say if the person decides to take action.
Kim,
Hey! This is getting into legal advice territory here, so all I can do is speculate, unfortunately. When I tested, I did not receive a confirmation email from WordPress that data was deleted (that process under Tools is a WordPress feature, not Ninja Forms- we just hook into it). I’m honestly not certain if further communication is a legal obligation on your part or not- Article 17 of the GDPR requires a ‘response’ to a request for data erasure within 30 days, but I’m not certain if that is legally met via simply erasing the data, or if further communication is required.
To be on the safe side, I’d tend to say to comply with requests as they come in and keep a detailed record of such. Then consult appropriate legal counsel on the particulars as you’re able. Sorry I can’t be more specific, but I hope that helps. I need to go to law school… :p
Cheers,
Quay
Hi, This is one of the best articles I’ve found so far but I think you’d need at least 2 consent options because what if someone wants a reply to a specific question about a product or service, but doesn’t want to be added to an email list for remarketing purposes. I appreciate it’s probably a given they do want to hear from you, but the example you give doesn’t really cover this.
Giles,
Hey! If you’re going to be using data collected under one premise (requesting a response to a question about a specific product or service) to target for remarketing, then you absolutely need to be transparent about that, provide info on how the data will be handled and used (tos, privacy policy links, etc), and request explicit consent for that.
To the best of my understanding, if the data is only going to be used for the stated purpose of the form and tos/privacy policy is linked to explaining handling/use etc, then additional explicit consent is not required. Submitting the form for the stated purpose with transparency on handling provided should be sufficient.
Here’s an ICO resource on consent that may help with the details of when consent is necessary, and when it isn’t: https://ico.org.uk/for-organisations/guide-to-the-general-data-protection-regulation-gdpr/lawful-basis-for-processing/consent/
Cheers,
Quay
Hi, great article and information, many thanks.
Like most, I have a ‘Contact us’ form on my websites which sends me an email. Other than responding to that email (by email or phone) I have no reason or desire to store that person’s data. Is there any reason why I can’t just have a simple paragraph like this next to the submit button on my form?
‘General Data Protection Regulations (GDPR). By submitting this enquiry form you are agreeing that the data you have completed can be used by {{COMPANY NAME}} to reply to your enquiry. Your details will be received as an email and will not be stored for any future marketing, promotion, newsletters or passed to any third party.
Jason,
That sounds good for expressing how the data will be used and acquiring consent. Linking to an actual privacy policy might be a cleaner option than housing that on the form, and is generally a good idea to have one anyway, but that’s up to your discretion to the best of my knowledge.
Since it sounds like you’ll be storing at least an email address (unless you’re using email actions to respond rather than storing?), you’ll need to be able to provide a channel for users that want to request what data you have on them and delete that data as well, as described in the article.
Cheers,
Quay
If we want to automate export but don’t want to delete request then what should we do?
Alex,
Hey! These appear as 2 separate actions within the form builder: Delete Data Request, and Export Data Request. Just use one and not the other 🙂
Cheers,
Quay Morgan
Hey, thanks for the updates, this is very helpful.
Question – I’m trying to complete my privacy policy, section Contact forms.
I have a very simple form that only requires name and email and I’ll set the submissions to expire after 90 days. This is what i got so far:
Thru the contact form, (website name) does collect the personal data you provide us with (specifically your name and email address). We store and retain this data for a period of 90 days. The information collected thru this form we may use to:
• to send you administrative communications, such as administrative emails, confirmation emails, technical notices, updates on policies or security alerts;
• to respond to your comments or inquiries;
• to provide you with user support;
• to protect, investigate, and deter against unauthorized or illegal activity.
Is that all I should mention? Does Ninja Forms collects any other data I don’t know about?
Thanks.
Yoka,
Using the Erase Personal Data feature will delete all pii associated with that address collected via Ninja Forms. Nothing will remain anywhere after that.
What you’ve written sounds good for communicating data usage in your privacy policy, with the caveat that I’m not legal counsel by any stretch of the imagination 🙂
Cheers,
Quay
Do you have to store the data in a database or in an encrypted location ?
Hi,
The data does not have to be saved within the database. Within your Ninja Form, you can delete/disable the Store Submission action to ensure that no data is saved to the database after submission.
Best regards,
Curtis
Hi Quay,
If we use the Ninja Forms to run a sign up form that collects sensitive customer info – do Ninja Forms have any access or visibility to that information considering we would be using your plugin to run it?
Thanks,
Enda
Enda,
Hey! Great question. No, we do not. We never view or record any data collected by your forms. The only data we ever collect, if you specifically opted-in on plugin install, is basic site telemetry like WordPress version, PHP version, and related metrics that help our development team plan. You’re opted out of that by default. If you’re unsure of your status on that, you can view and change it under Ninja Forms > Settings > Advanced Settings > Telemetry.
Cheers,
Quay
That’s great. Thanks for the feedback Quay. Much appreciated.
Thank you so much Quay for this informative article! We use WordPress for our blog and this definitely does help. This does help a lot.
Building on @Jennifer’s point about automated deletion — we’ve found that combining a manual expiry timer with a cron-based cleanup workflow saves us from having to remember to empty the Trash folder. Our setup runs a weekly check and permanently removes expired submissions, which closes the loop the article mentions.